 LeCoqRoti
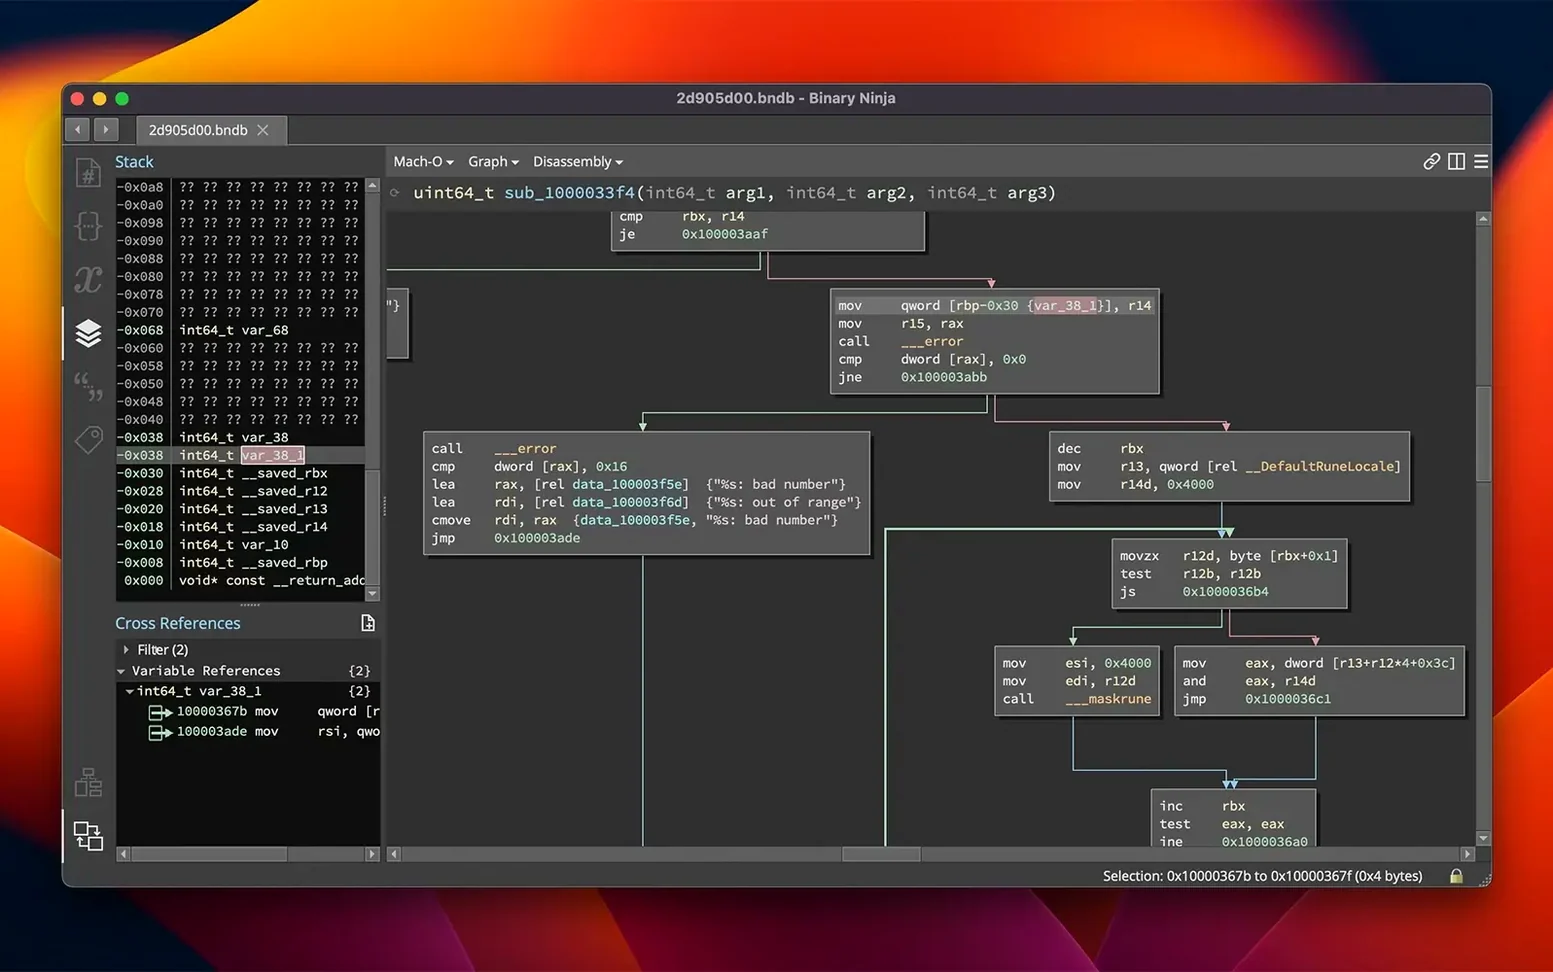
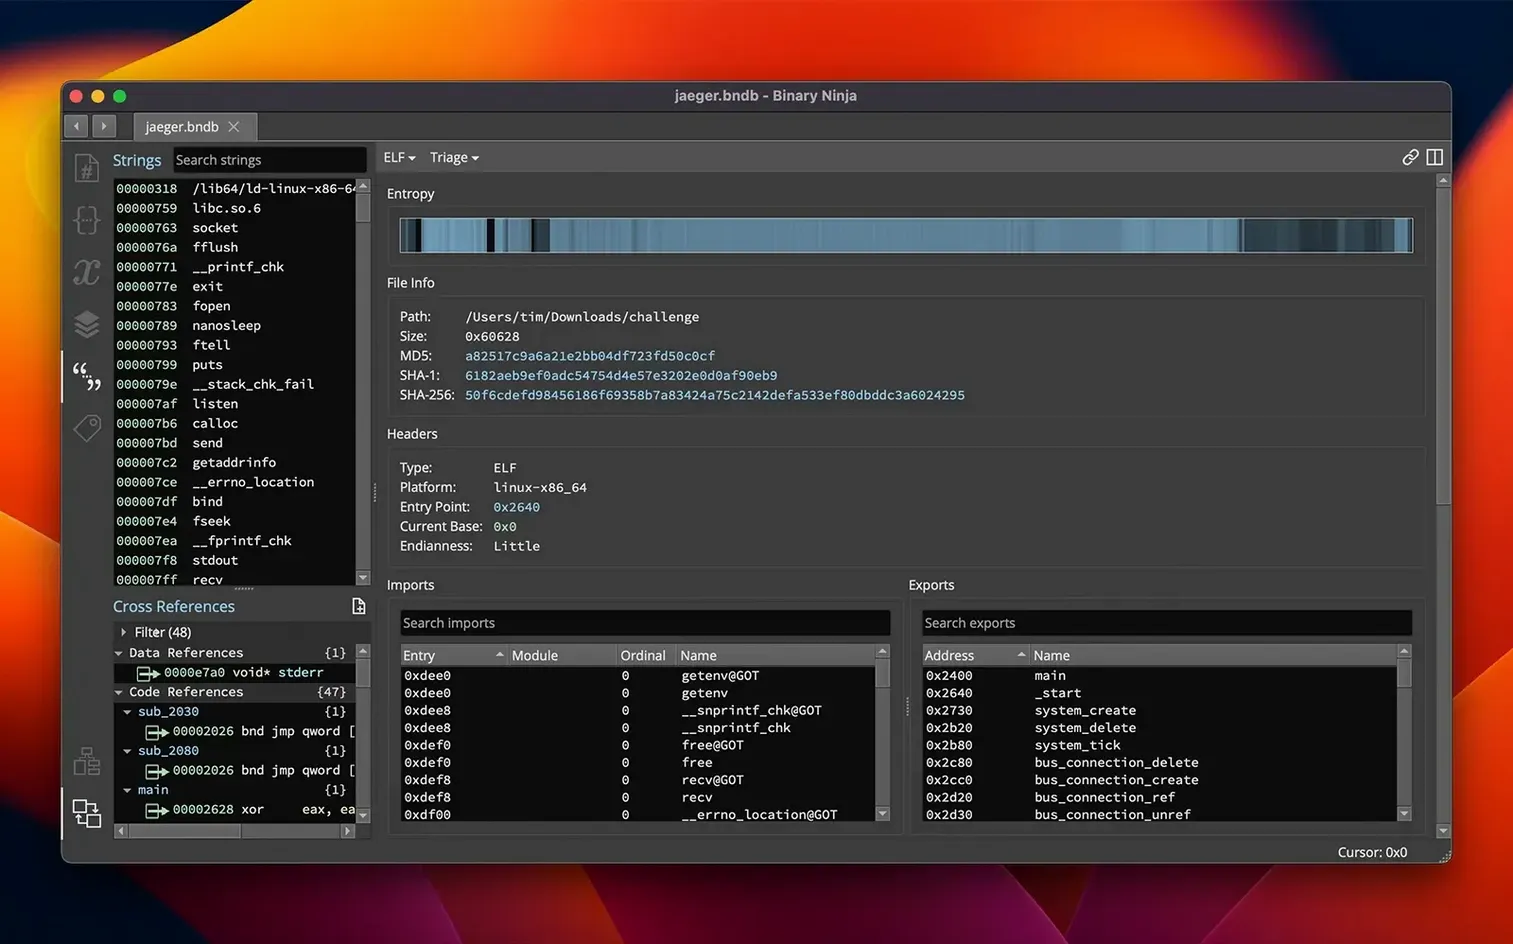
Binary Ninja is a reverse-engineering platform that combines a disassembler, a decompiler, and a binary analysis toolkit in a single application. Before installing, a few questions tend to surface.
Binary Ninja torrent — what the search really means
A query for a “Binary Ninja torrent” usually signals a developer evaluating the tool’s architecture support and decompilation quality before committing to it. The platform handles x86, x86-64, ARMv7, ARMv8/AArch64, PowerPC, 6502, Z80, MIPS, and the newly added TMS320C6x — so that evaluation covers a broad spectrum of targets.
Kick ninja crack — what it implies about patching
Searches around “kick ninja crack” often point to an interest in modifying binaries. Binary Ninja supports binary patching directly: you can edit assembly, apply preset patches, manipulate raw bytes in the hex editor, or compile C on the fly with the built-in SCC compiler.
1041 in binary — a typical conversion task
“1041 in binary” is the kind of quick mental conversion a reverse engineer performs constantly. The platform’s APIs for C++, Python, and Rust let you script those calculations and far more complex analyses, extending the tool from a simple hex converter into an automated reverse-engineering environment.
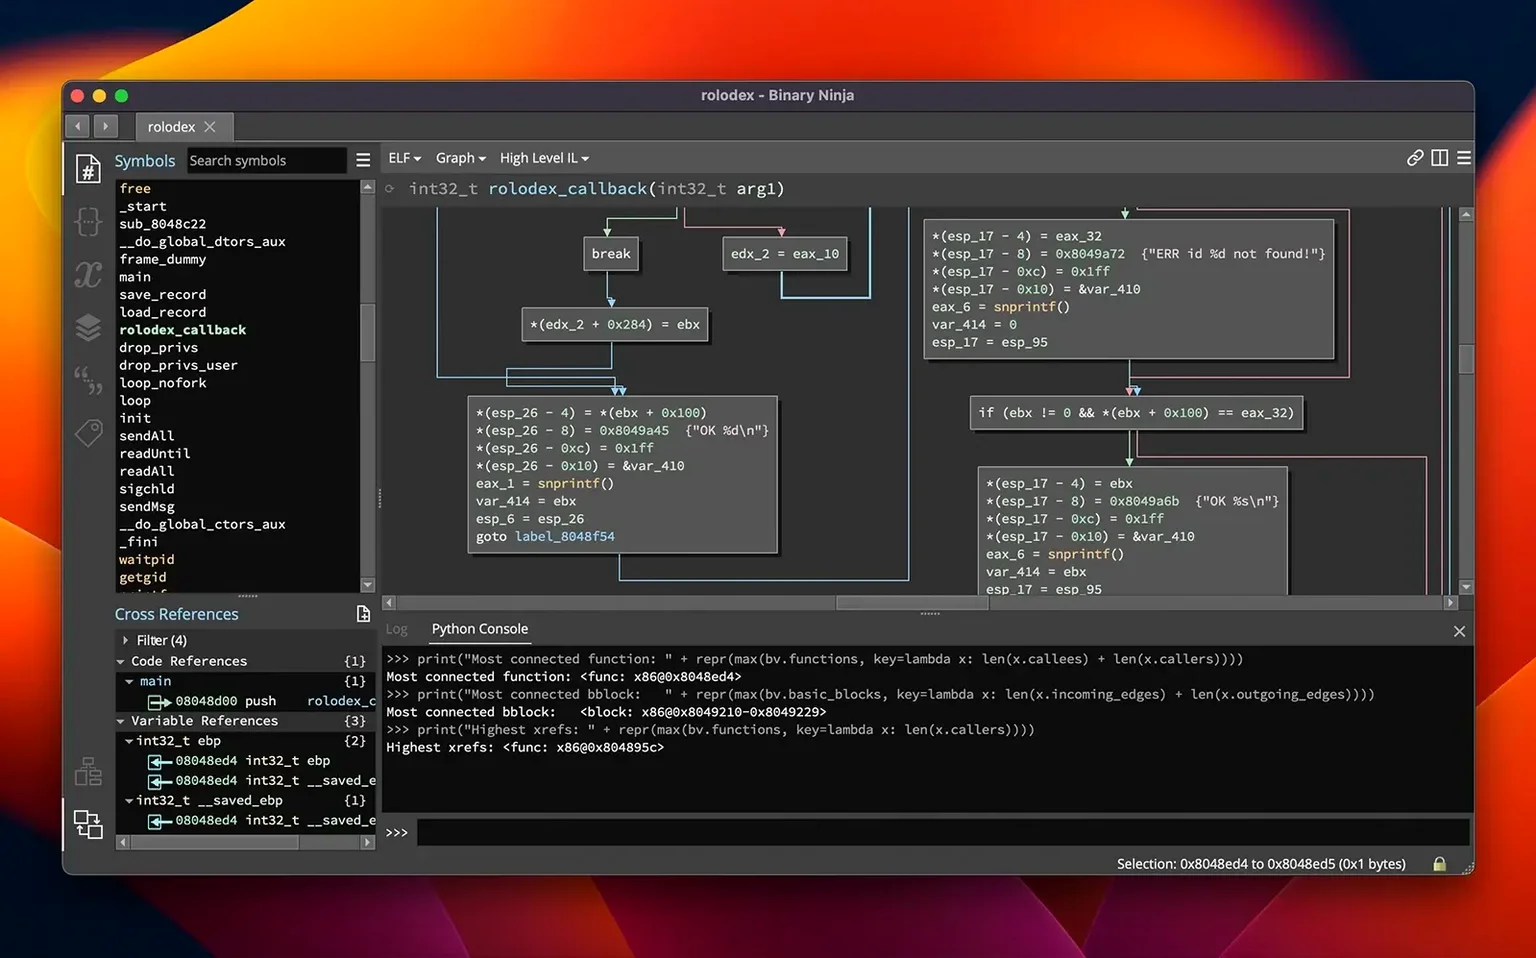
Small conveniences that surface with regular use are easy to overlook when you first open a binary. One is the cross-reference graph: holding X while hovering over a symbol opens a miniature graph that shows all callers and callees without leaving the current view — useful for tracing a function’s reach in a large codebase. Another is the type library quick-apply. Instead of manually defining every structure, you can import type libraries for common platforms (Windows SDK structures, standard C libraries) through a right-click in the types panel, then apply them across the binary with a single action. The hex editor synchronisation is also worth noting: selecting an instruction in linear view and switching to hex view places the cursor at the exact corresponding bytes, and editing those bytes updates the disassembly immediately. For those who work with multiple binaries at once, the tab memory means closing and reopening a file restores the exact cursor position, visible panes, and analysis state you left it in.
Workflow: tracing a network call from a suspect binary
Suppose you have a Mach-O executable that makes an unexplained outbound connection. Drop it into Binary Ninja and wait for linear analysis to finish. Open the symbols panel and filter for networking-related imports: connect, getaddrinfo, send. Clicking connect highlights every cross-reference in the disassembly. Pick the first reference in the user code section — not in a library thunk — and jump to it.
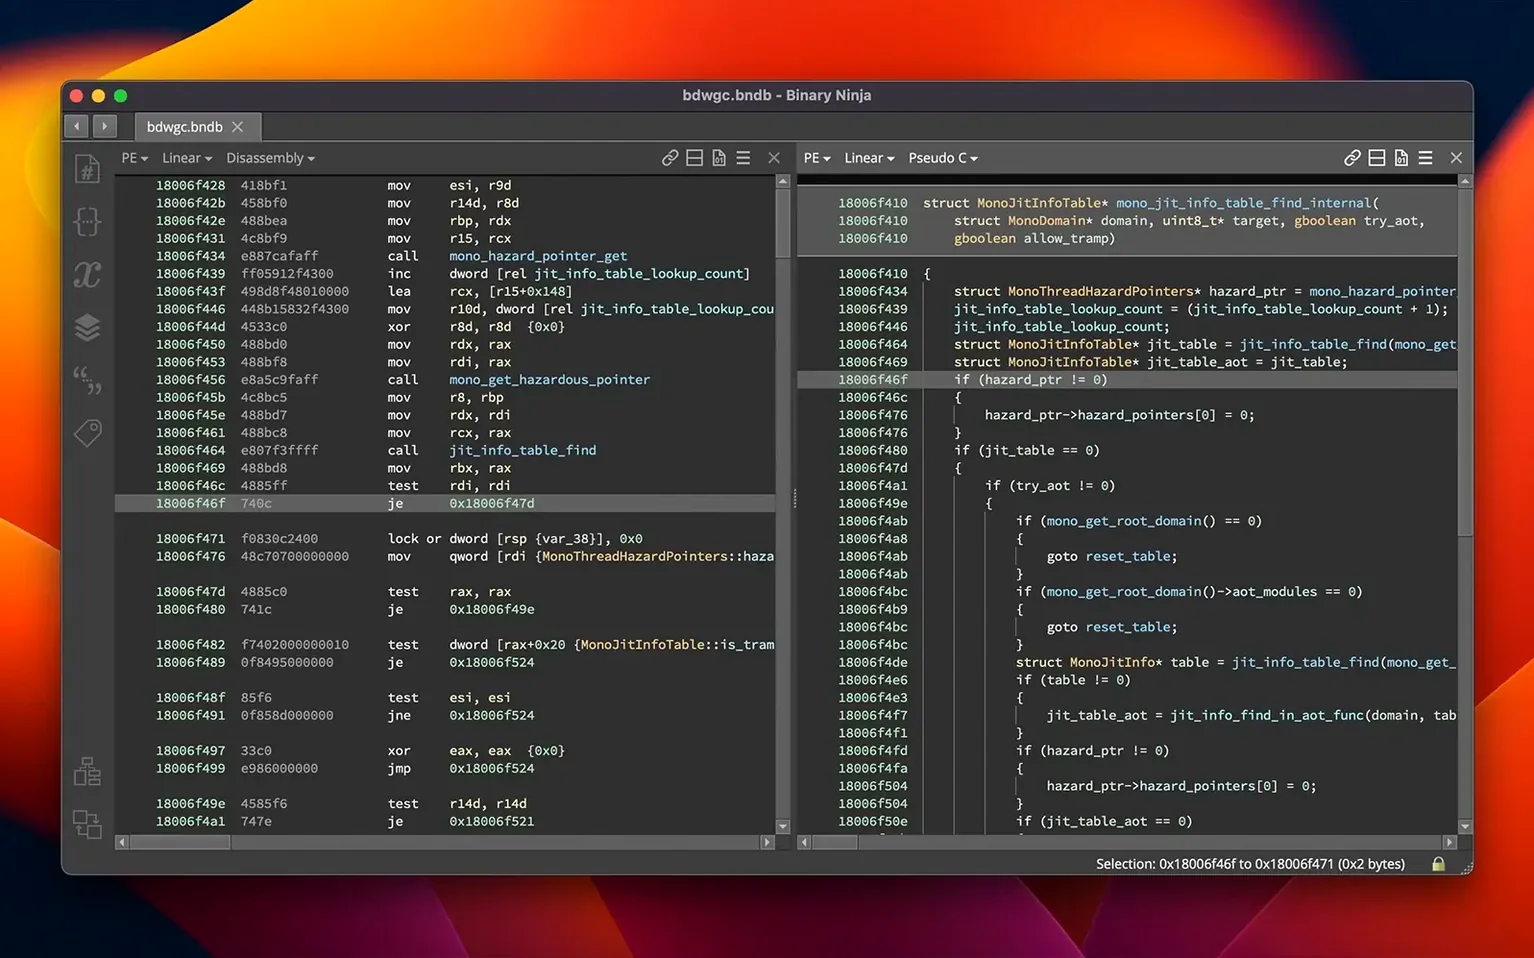
From the call site, trace backwards using the HLIL stack view. The decompiler presents a high-level representation of the function; you can rename variables like sockfd and sockaddr_in directly in the HLIL pane, and those names propagate automatically to the disassembly view and any other references. Follow the variable holding the address structure back to where it is populated. Usually you will find a call to inet_addr or a hardcoded IP pushed onto the stack. Right-click the immediate value, choose convert to hex or convert to string depending on the encoding, and the target address becomes readable.
Mark the function with a comment summarising the behaviour — right-click the function header, Edit Comment, and type something like “Beacons to 192.0.2.10:443, TLS handshake follows.” Open the entropy graph from the tools menu to check whether other sections contain encrypted or compressed blobs that might hold configuration data. If the binary uses a custom protocol, the script console (bound to ` by default) lets you run Python or C++ snippets against the current database, so you can extract and decode payload fields without leaving the environment.
Loop patterns lost in HLIL: forcing recognition with P
- Decompilation shows
jumpinstead of a loop. Binary Ninja’s HLIL can lift awhileorforloop if the control flow is clear, but obfuscated or compiler-optimised jumps sometimes defeat the pattern matcher. Select the region, pressPto define a function boundary manually, then right-click and choose Reanalyse. If that fails, patch ajmpto a conditional branch in the hex view and reanalyse; you can reverse the patch afterwards. - Type propagation stops at a library call. When a function returns a pointer whose type is not inferred, the downstream code fills with
void*casts. Open the type library panel, locate the correct prototype for the library function (for example,CFDataGetBytePtrfrom CoreFoundation), and apply it to the import symbol. The new type flows through all callers on the next analysis pass. - Plugins disappear after an update. Version 6.0 replaced the Plugin Manager with the Extension Manager. If an older plugin does not appear, its manifest may lack the updated compatibility key. Check the extension’s repository for a 6.0-compatible release, or open the extension’s
plugin.jsonand add the current API version string — though that is a short-term fix. The migration wizard in 6.0 handles this for most popular extensions. - The binary loads but architecture is misdetected. This happens occasionally with fat binaries or unusual container formats. Use File > Open with Options and specify the loader and architecture manually from the dropdowns. For a raw firmware dump, selecting Raw as the loader and setting the base address avoids a cascade of incorrect cross-references.
Those who arrive via a “Binary Ninja crack download” query often discover that the headless analysis mode suits automated pipelines elegantly. The command-line interface accepts a script argument, runs the analysis, and exports results — all without opening a window — which fits neatly into CI workflows and batch malware triage.
In short: the questions people ask before installing reveal exactly what the tool delivers — architecture coverage, direct binary modification, and a scriptable analysis engine.
Correspondence 0
Take a chair or join the table to send a letter.
No correspondence on this note yet. Letters are read before they appear.