 LeCoqRoti
Little Snitch is for the person who wants to know exactly what their Mac is saying to the outside world. A designer, a developer, someone who simply prefers to be asked before a new helper tool phones home. It sits quietly in the background until an application attempts to reach a server, then presents a clear alert with the details.
One task: tracing a helper tool’s home
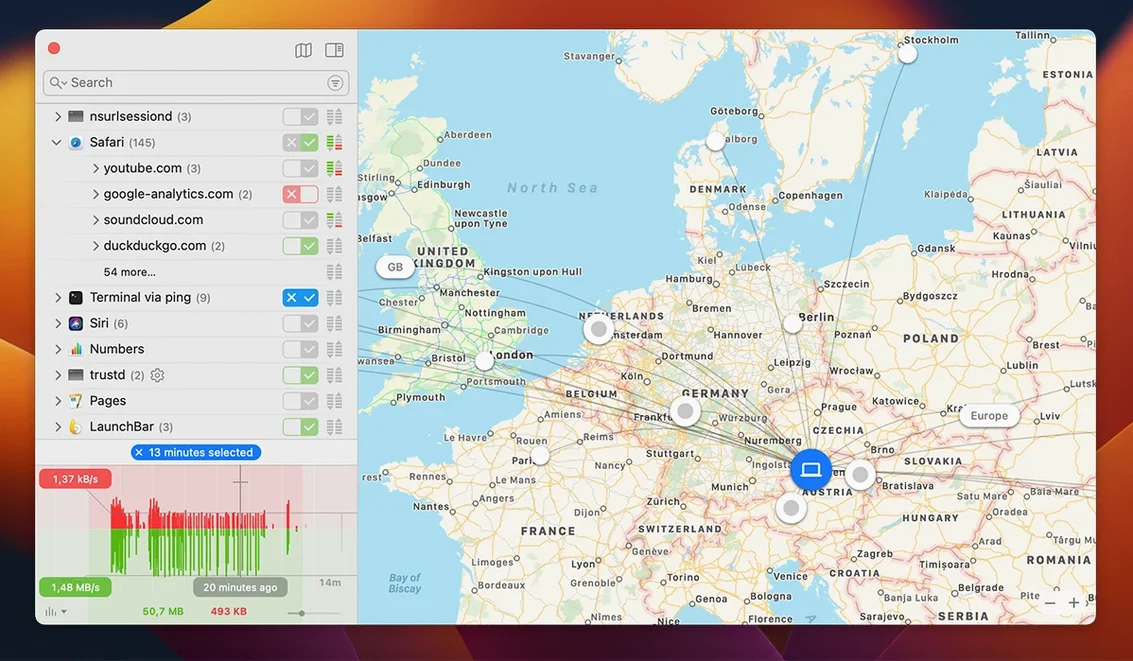
A common scenario with a new utility is wanting to see where it connects. The first connection attempt triggers a Little Snitch alert, showing the application name and the destination server. Rather than simply allowing or denying it, switching to the Network Monitor reveals an interactive world map. A line arcs from my location in Tokyo to a point in Frankfurt. The same data appears in an app-and-server list, with a traffic history chart that updates every hour, confirming that the tool only checks for updates once a day.
Rules: a decision made once
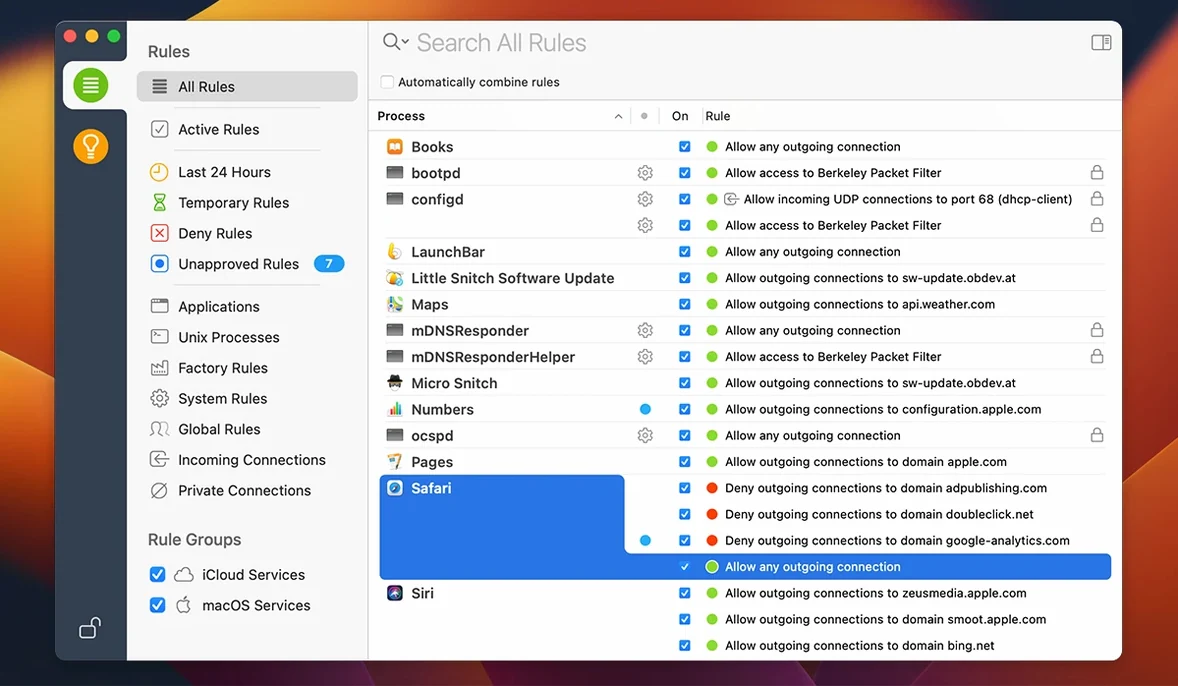
Each alert offers the chance to build a permanent rule. You can decide a connection is allowed only to a specific domain, on a particular port, or for a single session. Once created, the rule is remembered and applied automatically in the future. For times that require deep focus, a Quiet Mode postpones all notifications and decisions until later, letting you review a tidy stack of pending connections. The entire filtering engine now uses a modern architecture, leaving behind the older kernel-extension approach, and version 6.5 adds an experimental NAT64 implementation alongside encrypted DNS improvements. In short: the map and rule set turn a simple allow-or-deny choice into a genuine understanding of network activity.
First days: the sensible defaults to change
After installation, the initial alert flood can feel overwhelming. Every background service, every helper, every updater requests permission at once. The sensible approach is not to answer each one individually during the first hour. Instead, open Little Snitch’s preferences and enable Silent Mode temporarily. This lets connections proceed under a provisional allow-while-silent rule, while you go about your usual work. Later, when the system has settled, switch back to Alert Mode and review the collected connections in the Network Monitor. The map and the traffic list will show you which destinations your machine actually visited during a normal working day.
Another early adjustment concerns the alert presentation. By default, the alert sheet drops down from the menu bar, but if you work with a tiling window manager or simply dislike the intrusion, the notification style can be set to a compact banner instead. The banner shows the application name and the server address, with keyboard shortcuts to allow or deny without leaving the keyboard. For users running little snitch monterey-era habits — clicking “Allow” reflexively because the alert interrupts a flow — this banner mode encourages a brief pause before muscle memory takes over.
A practical tip for the first week: create a dedicated group in the rules window for Apple system services. Move all the automatically created rules for processes like trustd, nsurlsessiond and akd into it. This keeps the rule list legible when you later need to locate a custom rule you built for a third-party tool. The rule list’s search field accepts exact process names, and version 6.5 fixed a rare crash that occurred during that exact-match search, so the feature is now reliable.
Workflow: auditing a design tool’s update mechanism
Suppose a new design application promises it checks for updates once a week, but you notice the Network Monitor’s traffic volume chart spike every few hours. You want to verify what is happening without blocking the tool outright. Here is a start-to-finish approach using Little Snitch alone.
Open the Network Monitor and clear the traffic history to get a fresh baseline. In the rules window, locate the application’s existing rules — likely one broad “allow any connection” rule created during installation. Select it and change the action to Ask for the next 24 hours. The application will now trigger an alert on every connection attempt. Leave the Mac idle for an afternoon, then return to the Network Monitor. Sort the connection list by server name and look for entries from update domains. The hourly traffic history shows clear bars at two-hour intervals, not once a week. Clicking a server entry on the world map reveals the physical location: a cluster of connections to a data centre in Oregon, and another in Singapore.
Now build a precise rule. In the alert sheet, choose to allow connections only to the specific update domain, on port 443, and deny all others. Apply the rule permanently. The application continues to receive updates, but the unexpected background chatter stops. The traffic volume label in version 6.5 — renamed from “traffic amount” — gives a quick numerical readout of how much data those side connections were actually moving. In this case, it was negligible, but the audit itself was the point.
Version 6.5: what changed in daily use
The jump to version 6.5 brought several changes that affect everyday workflows, not just compatibility checkboxes. The most visible is the relabelling from “traffic amount” to “traffic volume” throughout the interface — a small language edit that makes the column header read more naturally in English and German alike.
Under the hood, encrypted DNS handling received a substantial improvement. For users who configure encrypted DNS profiles — whether through a VPN provider or a custom resolver — earlier versions could occasionally misinterpret the traffic type, causing connection alerts to show a generic IP instead of a meaningful domain name. Version 6.5 resolves this more reliably, so the Network Monitor now displays the actual domain being queried, even when the DNS traffic is encrypted. This is particularly helpful when you are tracing what a little snitch 6 alert for mDNSResponder or a third-party browser is actually resolving.
The experimental NAT64 implementation matters mainly to users on networks that employ IPv6-only addressing with a NAT64 gateway — certain corporate environments and some mobile hotspots. Previously, Little Snitch could not inspect connections traversing a NAT64 translation, leaving a blind spot in the network map. With the experimental support active, those connections appear in the app-and-server list with their synthesised IPv6 addresses, and the map can place them geographically. It is off by default and must be enabled in the advanced preferences, but for the subset of users who need it, it closes a meaningful gap.
App bundle integrity monitoring is a quieter addition. While an application is running, Little Snitch now periodically checks whether the app bundle on disk has been modified. If a previously trusted application is altered — for example, by a malicious helper replacing its binary — the existing rules no longer apply silently. The next connection attempt triggers an alert flagged with a bundle integrity warning, letting you re-evaluate the application before its traffic continues. For anyone who has ever downloaded a Little Snitch crack or modified a helper tool manually, the alert provides a clear signal that the application is no longer what it was when the rule was created.
Scenario: the photographer’s upload evening
A photographer returns from a shoot in the mountains and connects her MacBook to the hotel Wi‑Fi. She has 12 gigabytes of raw files to back up to a cloud storage service, and the hotel network is slow enough that she wants to be certain no other application is consuming bandwidth while she works. She opens the Network Monitor and watches the connection list populate. Safari is idle. Mail is idle. The cloud sync client opens a single connection to a server in Amsterdam and begins uploading at a steady 800 kilobytes per second, confirmed by the traffic volume column.
Half an hour in, a new entry appears: a photo cataloguing application has woken up and is attempting to connect to a telemetry service. The world map draws a line from her current location to a server in Northern California. She selects the entry, clicks to create a temporary deny rule valid for the next six hours, and the connection drops. The upload continues uninterrupted. Before she sleeps, she opens the hourly traffic history and sees a clean block of upload throughput for the cloud client, a single small spike for the telemetry attempt that was denied, and nothing else. The evening’s bandwidth went exactly where she intended it to go.
Correspondence 0
Take a chair or join the table to send a letter.
No correspondence on this note yet. Letters are read before they appear.