 LeCoqRoti
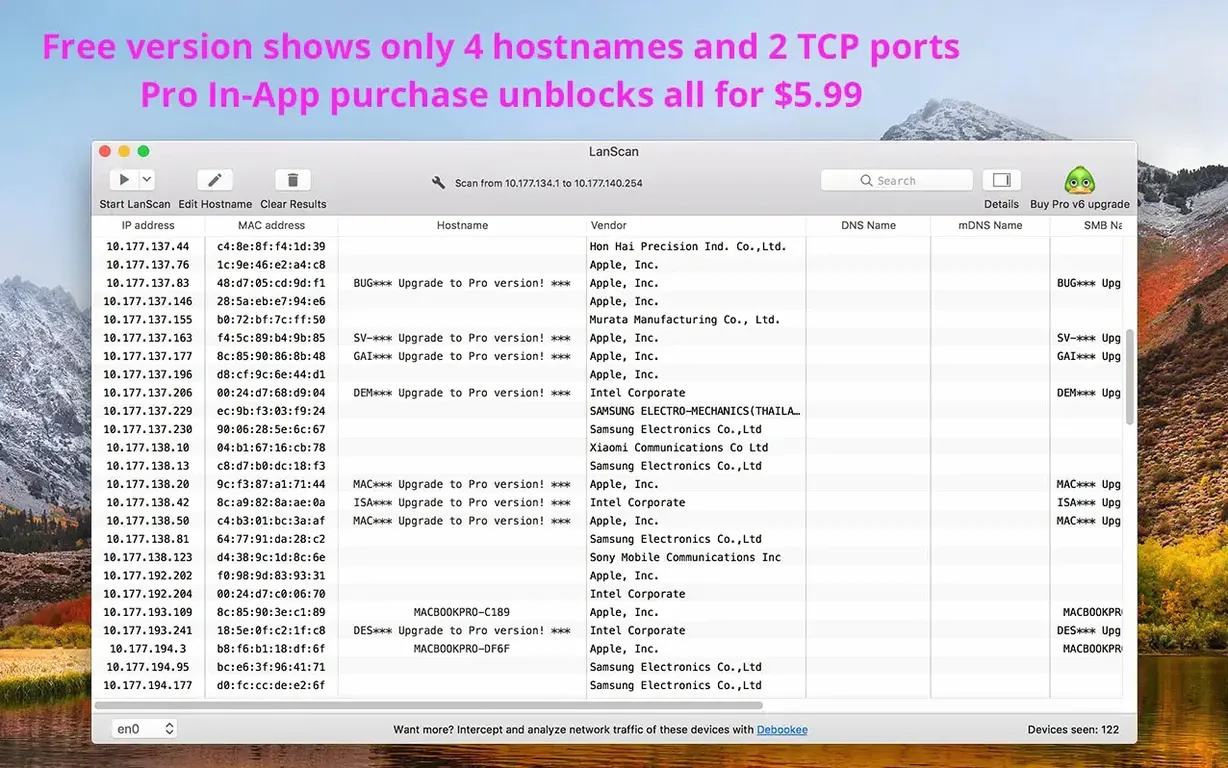
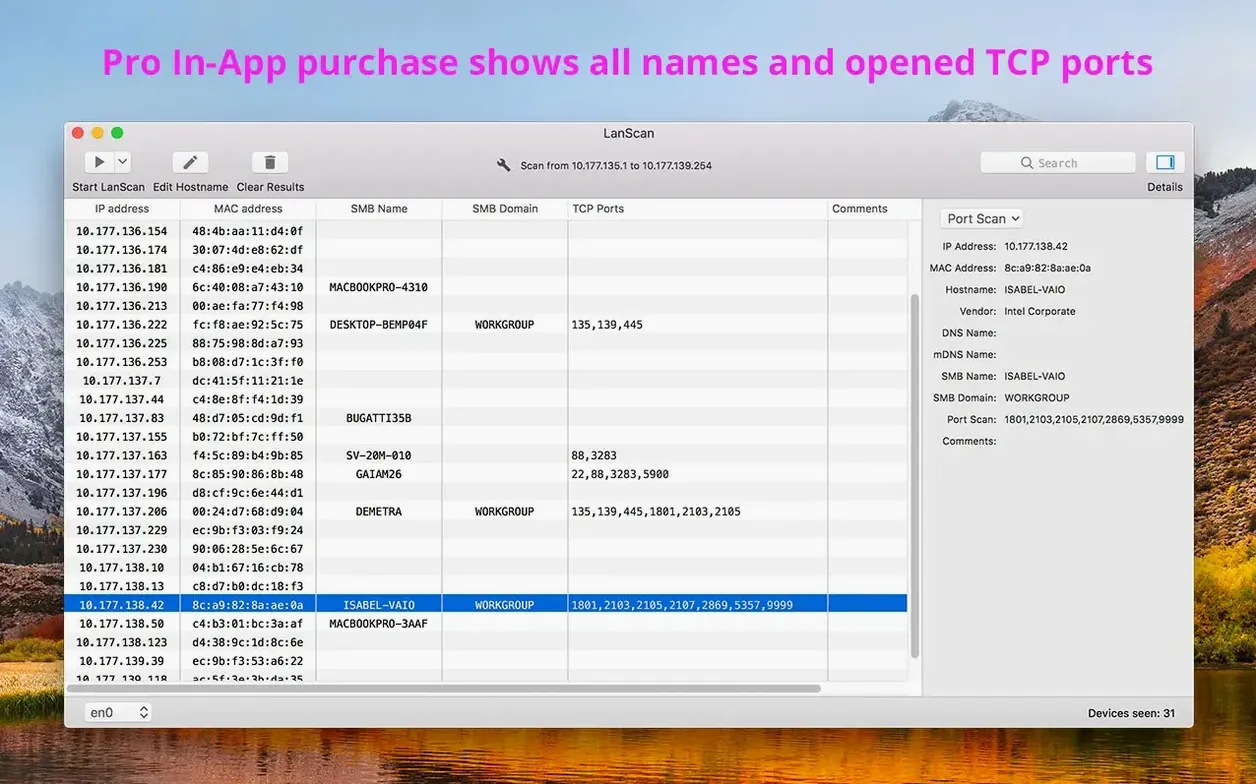
System administrators and the perpetually curious tend to reach for LanScan when they need more than a simple list of online devices. It is the kind of tool that rewards a second look: beneath a calm, column-driven interface sits a scanner that understands both IPv4 and IPv6, and that gathers its data through a considered mix of Ping, SMB, and mDNS packets. The result is a device table that feels precise rather than chatty.
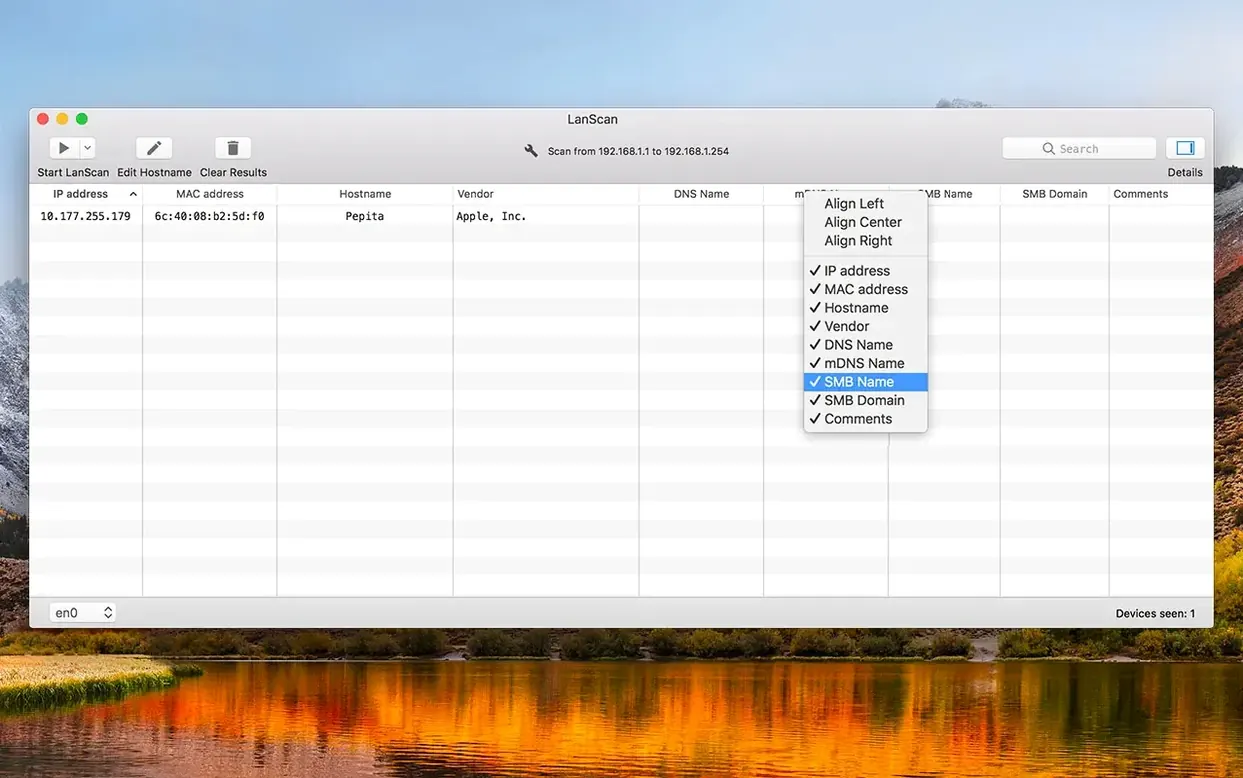
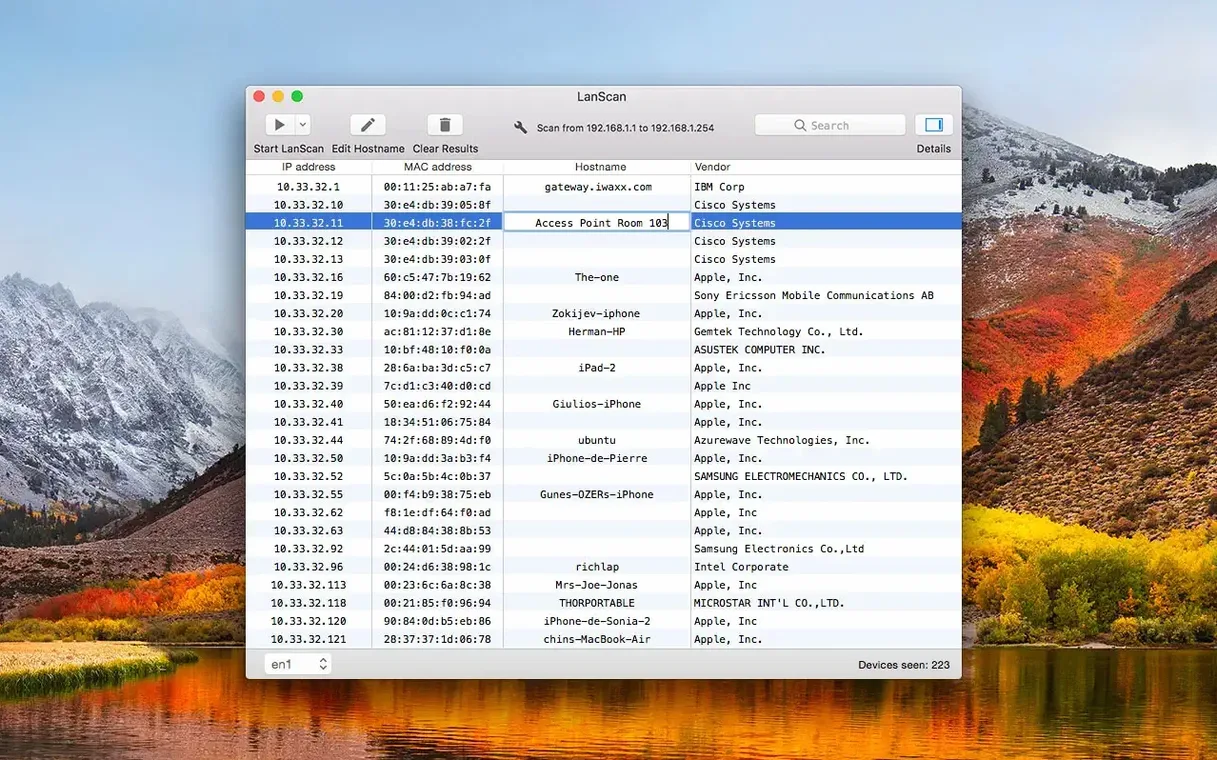
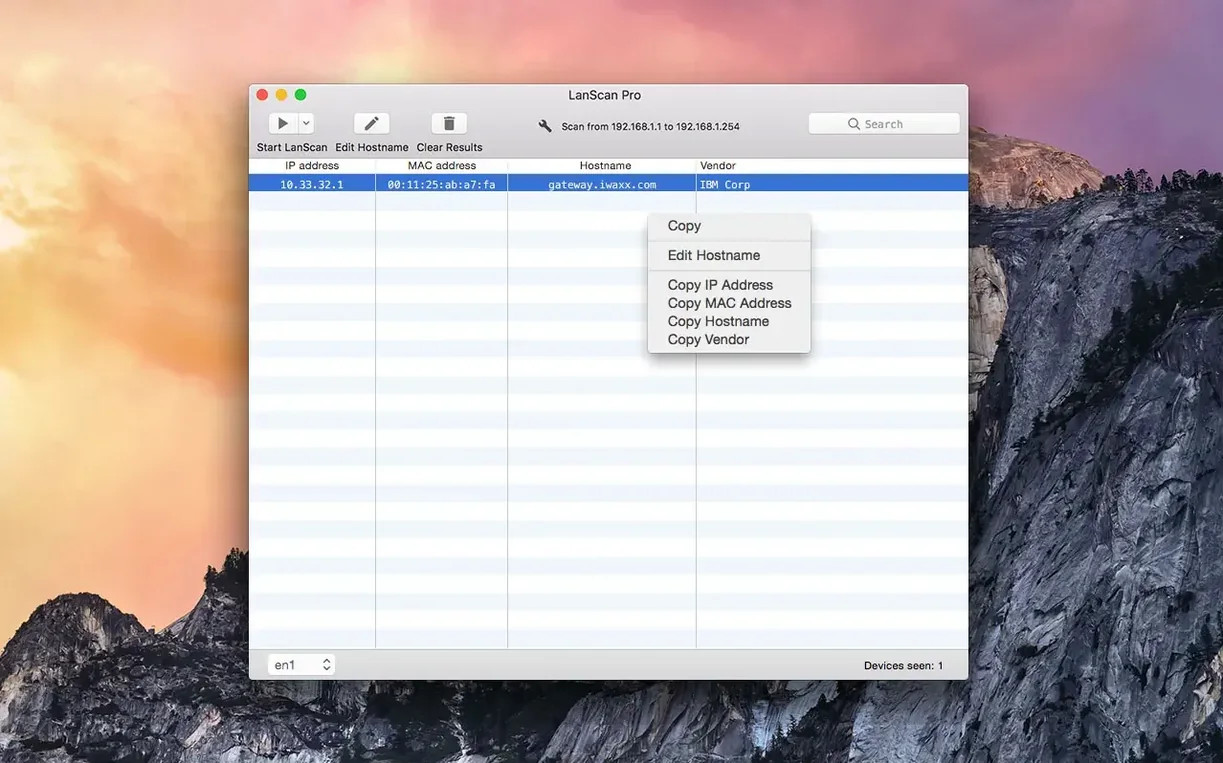
Each discovered host earns a row with its IP and MAC addresses, a vendor name pulled from the OUI database, and up to four associated host names. A user can manually edit any host name or attach a custom comment to a device—a small detail that turns the app from a one-off discovery tool into a living record of a network. Columns hide or reveal themselves with a click, so the view stays focused on what matters for the task at hand.
Interface detection is automatic: AirPort, Ethernet, and any virtual interfaces present on the Mac appear without configuration. For public range scanning, the same three protocol probes go to work, and the findings can be exported as a clean CSV file when the session ends. There is no dashboard pretence here, just a fast, legible report on what is connected.
Running on Apple Silicon and Intel Macs from macOS 11 onward, LanScan feels like a utility that has been sharpened over time for people who read their networks closely. In short: it trades surface-level friendliness for depth, and the trade works.
It is worth placing LanScan alongside a couple of better-known Mac network scanners to see where its strengths settle. Angry IP Scanner is probably the most direct comparison: cross-platform, open-source, and driven by a similar no-fuss philosophy. Where they differ is in the quiet polish of the Mac-native experience. Angry IP Scanner feels like a Java tool that happens to run on macOS; LanScan feels like it was written for it. The latter pulls in vendor names automatically from its built-in OUI database, resolves up to four host names per device without extra configuration, and handles IPv6 as a first-class citizen — something the current stable Angry IP Scanner simply does not do. For a network that has already begun its slow migration to v6, that single difference can be decisive.
Fing, the desktop version, brings a more consumer-facing design and a heavier emphasis on device recognition and internet-speed testing. It is pleasant to use but leans toward home-network storytelling rather than the kind of raw, every-packet-counts inspection that LanScan offers. Fing's interface groups devices into cards and categories; LanScan gives you a dense, sortable table where a single glance can confirm an unexpected MAC address. Neither approach is wrong, but a network administrator staring at a /23 range will probably prefer the table. NetScan sits somewhere between the two, with a capable scanner and a slightly dated interface; it handles the basics well, though its feature set has not kept pace with the quiet IPv6 groundwork that LanScan has already laid.
A working session: tracing a stray device
The morning starts with a ticket about a device hogging bandwidth on the guest VLAN. I open LanScan on a Mac connected to that subnet. The interface list populates instantly: the Ethernet adaptor and a single virtual bridge are pre-selected, because the app reads the system's active interfaces without asking. I leave the default scan range — the whole local subnet — and click the scan button.
The first phase is almost entirely ARP traffic, visible only as a quickening row count in the bottom status bar. Within four seconds twenty-three devices appear. Each row fills left to right: IP address first, then MAC, then the vendor column resolves from the OUI database — a column I keep narrow because I am usually hunting for the one manufacturer that does not belong. A TP-Link MAC sits where the inventory says only Aruba access points should live. The host name column remains blank for that row, so I right-click and trigger a manual mDNS and NetBIOS probe. A name resolves: it belongs to a smart television someone brought from home and plugged into a conference-room port.
I add a comment directly in the row — "unauthorised TV, port 12" — and then open a custom URL template that LanScan fills with the device's IP address, launching the television's embedded web interface in Safari. The whole session, from launch to identification to browser-based configuration page, takes less than a minute. Before closing the app, I export the subnet view as a CSV file and attach it to the ticket. The comment column survives the export, so the next person reading the file sees more than raw addresses.
Resources stay low: 45 MB during a typical subnet scan
On an Apple Silicon Mac, the application opens in a single bounce. Memory use during a scan of a typical /24 subnet hovers around 45 MB, rising gently to perhaps 60 MB when scanning a wider public range with hundreds of hosts. The CPU graph shows a brief spike during the ARP phase, then flattens to near-idle as the app waits for responses. I have not seen it beachball, even when scrolling through a table of over four hundred devices — the column sorting and hiding are responsive enough that the interface never feels like it is catching up with the data underneath.
Stability over a full working day is uneventful in the best sense. Leaving LanScan open between scans does not produce memory creep, and switching between a Wi-Fi and a wired interface — a moment where lesser network tools sometimes lose their grip on the adapter list — triggers a clean re-detection. The only perceptible pause happens during a public-range scan when the app switches from ARP to its Ping/SMB/mDNS triplet; that pause is a design choice, not a performance shortfall, and it lasts barely two seconds. For a utility that spends its life throwing packets into subnets, it runs with a composure that makes it easy to forget it is there — until you need it again.
No kernel extensions: probes use standard Mac frameworks
Does LanScan need to install a kernel extension or a packet-capture driver? No. It works entirely within the standard networking frameworks available to a sandboxed Mac app. The ARP, Ping, SMB, and mDNS probes all travel through the usual user-space channels, which is why the first launch requires no special permission beyond what any network-capable application already holds.
Will it scan a remote subnet, or only the local one? Both. Local scanning relies on ARP and is fast. For a remote or public range, you type the subnet manually — anything from a single IP to the full IPv4 space — and LanScan switches to its three-protocol probe method. The trade is speed for reach, and the app makes that switch transparently.
Can I use it to inventory a mixed IPv4/IPv6 network? Yes, that is one of its quiet advantages. The scanner handles both address families in the same scan session, so a dual-stack device appears with both its v4 and v6 addresses alongside the same MAC and vendor record. No secondary tool or separate scan pass is needed.
What does the CSV export actually contain? Every visible column: IP address, MAC address, vendor, up to four host names, the SMB domain if detected, any custom comment you have added, and the custom URL if one is configured. Columns you have hidden in the interface stay out of the export, so you can shape the output by adjusting the view beforehand. The file opens cleanly in Numbers, Excel, or any plain-text editor.
Correspondence 0
Take a chair or join the table to send a letter.
No correspondence on this note yet. Letters are read before they appear.